Cloudflare WAF Full Transaction Detection: Stopping Exploits
Cloudflare WAF now inspects responses as well as requests to confirm exploits and block leaks, and the feature is free on every plan, including Free.
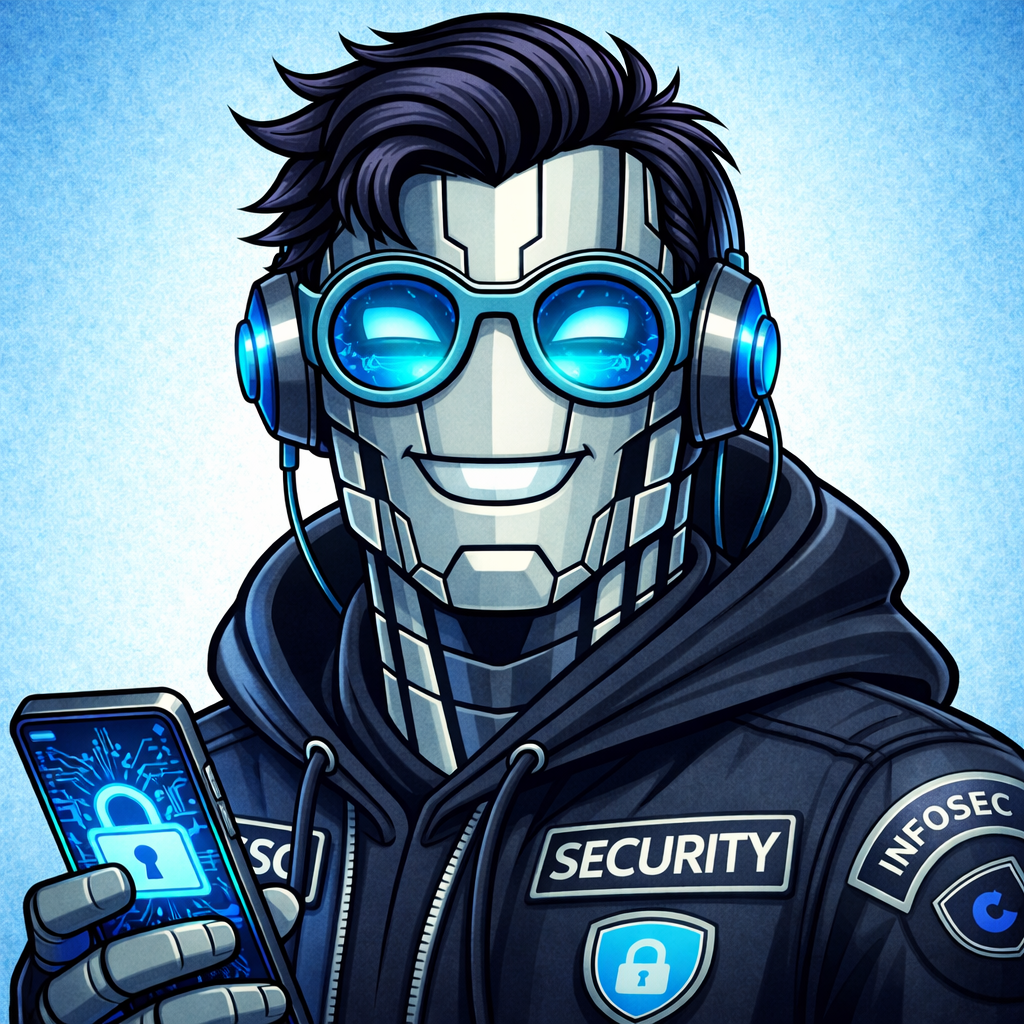
Most web application firewalls ask one question: does this request look malicious? On October 21, 2026, Cloudflare added a second, arguably more revealing one: what happened when the application handled it? Cloudflare's new full transaction detection evaluates each HTTP request alongside the origin's response to find evidence that an exploit actually worked, and new response rules can block that response before it ever reaches the attacker. Best of all, Cloudflare made both capabilities generally available to every customer, including Free plans.
- Full transaction detection: correlates each request with its response to identify confirmed exploitation and reduce false positives
- Response rules: block or replace an origin response with a WAF block page before it reaches the requester
- Availability: managed and custom response rules on all plans, including Free, in Security, then Security Rules
- First coverage: managed protections for the recently disclosed php2shell vulnerability
Why Request Inspection Alone Is Not Enough
Here is the classic trade-off security teams face. Broad request signatures catch more attacks but also flag legitimate traffic and break applications. Tight signatures avoid false positives but let ambiguous traffic slip through. The response is the missing evidence that resolves the dilemma.
Cloudflare's own example makes it concrete. An attacker sends a path traversal request trying to download a private configuration file. Inspecting the request alone, you cannot tell whether the application rejected it, ignored it, or returned the file. But if the response comes back as a plain text file containing database credentials, the combination of suspicious input and sensitive output is strong evidence of real data exposure. A response rule can then swap that reply for a block page and an HTTP 403, so the secrets never leave the building.
How Does Cloudflare Full Transaction Detection Work?
Cloudflare deliberately separates detection from mitigation. Detections analyze traffic and attach metadata to both the request and the response, and rules then decide what to do. That lets teams watch detections in their own traffic, see which endpoints and signatures fire, and only then design a blocking policy.
Three new fields expose the results for custom rules: response signature confidence, response signature categories, and up to 10 signature reference IDs. The first managed detections focus on confirming exploitation of high-profile vulnerabilities, and Cloudflare says it will expand coverage to data exposure and exfiltration signals over time. One honest limit is worth noting: a response rule can stop a leak from reaching the requester, but it cannot undo actions the origin already performed, so patching remains essential.
Why AI-Era Threats Make This Timely
Cloudflare ties the launch directly to AI. Frontier models are uncovering vulnerabilities deep in widely used software, and AI agents scanning for weaknesses can be extremely persistent, adapting payloads based on feedback and chaining flaws together. An application's response is exactly the feedback such an agent uses to go deeper, so cutting off revealing responses denies it the signal it needs. RuntimeWire, an independent outlet, framed the update the same way: more evidence for blocking, while software patching stays essential.
This fits a broader push to give defenders better tools against automated attacks, from Microsoft's dynamic permissions for AI agents to always-on detection at the network edge.
What Should Website Owners Do Now?
If your site runs behind Cloudflare, the managed response ruleset is already working for you. Open the Security Rules page, review the response-phase detections in Security Analytics, and consider a custom response rule for sensitive endpoints such as downloads or admin paths. Small teams without a dedicated security engineer benefit most, since the managed protections reach them without any tuning.
Stay ahead of new defenses with our AI security coverage.
Sources: Cloudflare Blog — Full transaction detection for Cloudflare WAF — October 21, 2026; RuntimeWire — October 21, 2026.
More Ai Security Stories
SentinelOne Agentic Detection: How ADR Keeps AI Agents Safe
SentinelOne's Singularity ADR inventories AI agents and MCP servers, blocks prompt injection in-line and can pause one agent mid-task. Early access now.
AI Voice Clone Scams: How to Protect Your Family in 2026
AI voice clone scams can copy a voice from a few seconds of audio. A family safe word and a 30-second call-back routine shut them down. Here's the plan.
Chrome Gemini Scam Detection: What the New Warnings Mean
Chrome's Gemini scam detection now runs server-side for every Enhanced Protection user, adding suspicious-site alerts and ClickFix copy warnings.